Ready for AI?

The Security and Governance Questions to Answer Before You Scale

Ensure your organisation is prepared to confidently scale AI by addressing essential security and governance questions before deployment.

13 October 2026 | 10:30 -11:30 am

Many organisations are eager to leverage AI tools, such as Microsoft 365 Copilot, to enhance efficiency and save time. However, they often lack clarity on which AI tools are currently in use, what information staff can access, and who is responsible for approving higher-risk applications. Simply having an enterprise license does not address issues like oversharing of files, unclear ownership, or unchecked outputs.


The government’s 2026 sector AI adoption plan reports that 43.4% of professional and business services firms were using AI in December 2025, a significant increase from 31.4% a year earlier. This highlights the critical need for robust governance as organisations scale their AI initiatives and address gaps in organisational readiness.

Secure your place today

Why attend

Join Advania’s Senior GRC expert, Raghbir Basra for this focused webinar, where we will address the significant challenges organisations encounter as they embrace AI.

Whether you’re preparing for an AI rollout or looking to enhance and tighten your current AI governance practices, you’ll leave with actionable insights and practical guidance to navigate the complexities of AI adoption securely covering:

  • Prevent Costly Breaches
  • Clarify Accountability
  • Enhance Decision-Making
  • Mitigate Emerging Risks
  • Prepare for Regulatory Scrutiny
  • Proactively Manage Incidents

Meet the speaker

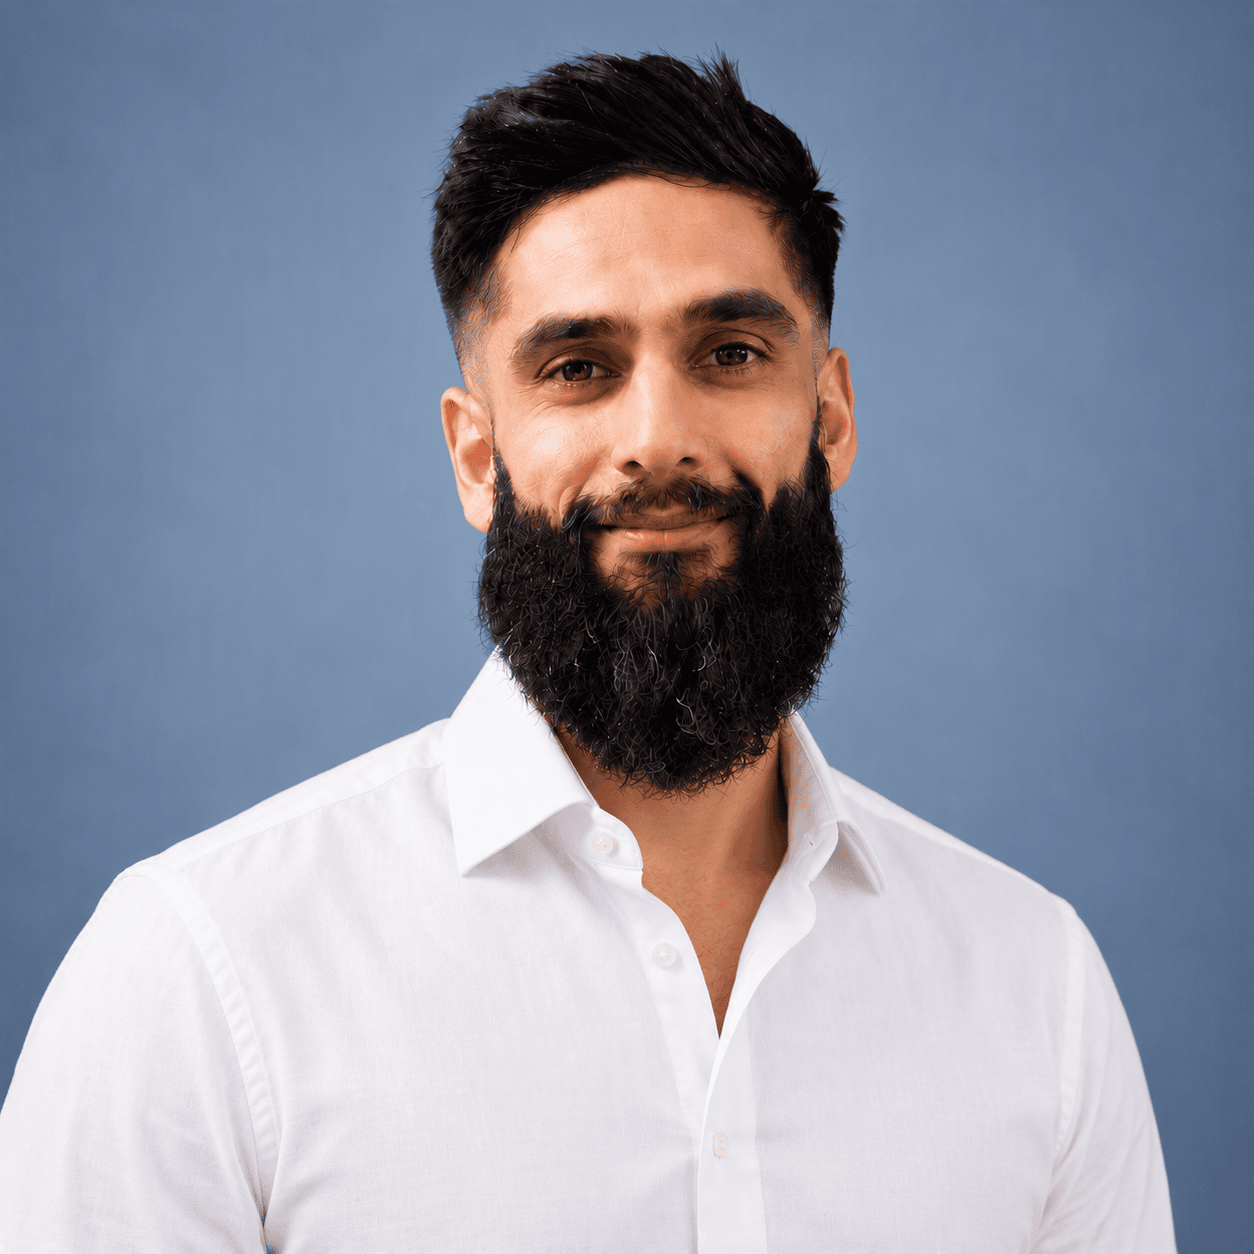
Raghbir Basra

Senior GRC Consultant

A Senior Governance, Risk and Compliance Consultant at Advania UK, specialising in security frameworks, security and data regulations. Works with organisations of all sizes to assess their current security arrangements, understand business and legal requirements and plan and implement improvements.

Raghbir’s experience covers advisory and implementation services, including security assessments, cyber strategy, policy development and virtual CISO support. He supports organisations from identifying gaps and defining requirements through to implementing controls and establishing ongoing governance, working with business leaders and technical teams to align security and compliance activities with business needs, regulatory obligations and the risks they face.

What you'll learn

  • Identifying Confidential Information: Understand how to recognise confidential data and determine appropriate access levels.
  • Protecting Sensitive Information: Gain an understanding of how labels, DLP and Access Controls can support the business rules.
  • Managing Access Permissions: Gain insights into ensuring that staff only access information necessary for their roles by regularly reviewing SharePoint and Teams permissions and removing overly broad access.
  • Governance, Risk and Compliance: Define acceptable AI usage, establish information-handling rules, and identify required controls through comprehensive risk, policy, and supplier reviews. Assessments based on NIST CSF or ISO 27001 can create a robust baseline, while a focused AI review can produce prioritized findings and management playback.
Reserve your place today and discover how to scale AI confidently with the right security, governance, and compliance foundations.

Registration form